Giveaway: https://www.tradepub.com/free/w_wile925/
Download: w_wile925.pdf – mirror
Offered Free by: Wiley
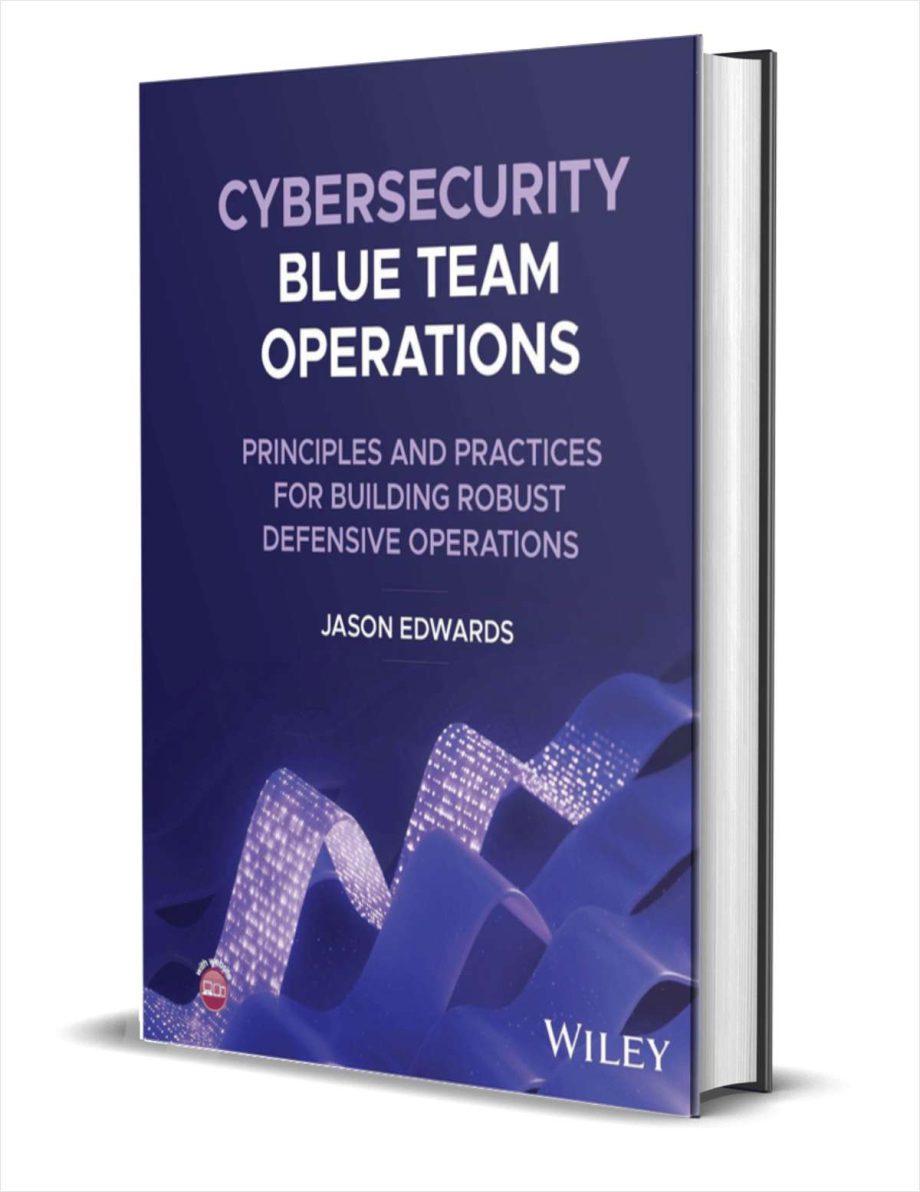
If you work in IT security or are building toward a career in cyber defense, this is the kind of resource that rarely shows up for free. Cybersecurity Blue Team Operations: Principles and Practices for Building Robust Defensive Operations is a deep, practical guide that walks you through everything a modern blue team needs to know, from setting up security operations centers to responding to live threats. At a retail value of $118.95, getting it at no cost is a genuine win for anyone serious about defensive security.
Key features
- Blue team methodology: Learn the structured approaches security teams use to monitor, detect, and respond to threats in real enterprise environments.
- Threat detection and hunting: Understand how to proactively search for adversaries already inside your network before they cause damage.
- Incident response frameworks: Follow proven playbooks for containing, eradicating, and recovering from security incidents efficiently.
- Security operations center (SOC) design: Get practical guidance on building and running a SOC that scales with your organization.
- Log analysis and SIEM usage: Master the art of correlating log data to surface meaningful alerts and reduce alert fatigue.
- Vulnerability management: Learn how to prioritize and remediate weaknesses before attackers can exploit them.
- Real-world case studies: Apply concepts through scenarios drawn from actual defensive operations, making theory immediately actionable.
Who is it for
This book is ideal for SOC analysts, IT security administrators, and network defenders who want a structured, authoritative reference for their daily work. It is equally valuable for cybersecurity students and career changers who are preparing for roles like security analyst, threat hunter, or incident responder. If your organization is building or maturing a defensive security function and you need a practical operations guide that goes beyond certification prep, this is exactly what you need. It also suits CISOs and security managers who want their teams aligned on consistent, principled defense practices.
How it compares
- The Practice of Network Security Monitoring by Richard Bejtlich: A well-respected classic focused specifically on network traffic analysis and NSM methodology, making it narrower in scope than a full blue team operations guide.
- Blue Team Handbook by Don Murdoch: A popular field reference formatted as a condensed quick-reference guide, great for experienced practitioners but less suited to systematic, principles-based learning.
- Applied Incident Response by Steve Anson: Concentrates deeply on the incident response lifecycle and Windows forensics, offering strong depth in that lane but limited coverage of broader SOC operations and threat hunting.
- CompTIA CySA+ Study Guide: Vendor-neutral exam prep that covers blue team concepts at a certification level, useful for testing but not structured as an operational deployment reference.
Cybersecurity Blue Team Operations sits in the space between a quick field handbook and a narrow deep-dive, offering broad, principled coverage of the entire defensive security function. It is the right pick for professionals and teams who want one authoritative, end-to-end operations reference rather than a collection of specialized titles.